Safer than a key. Private by design.
SafeXS was built from the ground up with modern cryptography, locks that are never on the Internet and a separate system for every customer. Here is how we protect your doors and your data.
What happens when you tap “open”
In about a second, three parties check each other: your phone, your lock system and the lock itself. Nothing in this chain can be copied and used again.
Your phone proves who you are
Your account is bound to your own phone and protected by a two-step login. The app only shows locks you may open, at the times you may open them.
A one-time, signed command
Your lock system issues an encrypted, digitally signed command with a time-based one-time code. Offline, the lock adds its own challenge that the phone must answer.
The lock checks, then opens
The lock verifies signature, code and validity itself, over Bluetooth, and only then opens. A recorded command is worthless a moment later.
Security that doesn’t depend on one single measure
Every layer is designed to hold even if another one fails.
Locks without an Internet connection
Locks and controllers only speak Bluetooth with authorised phones. Without an Internet connection, there is nothing to attack over the Internet.
Strong cryptography
TLS 1.2/1.3 between app and server, encrypted opening commands, Ed25519 digital signatures and time-based one-time codes per lock.
Keys that expire
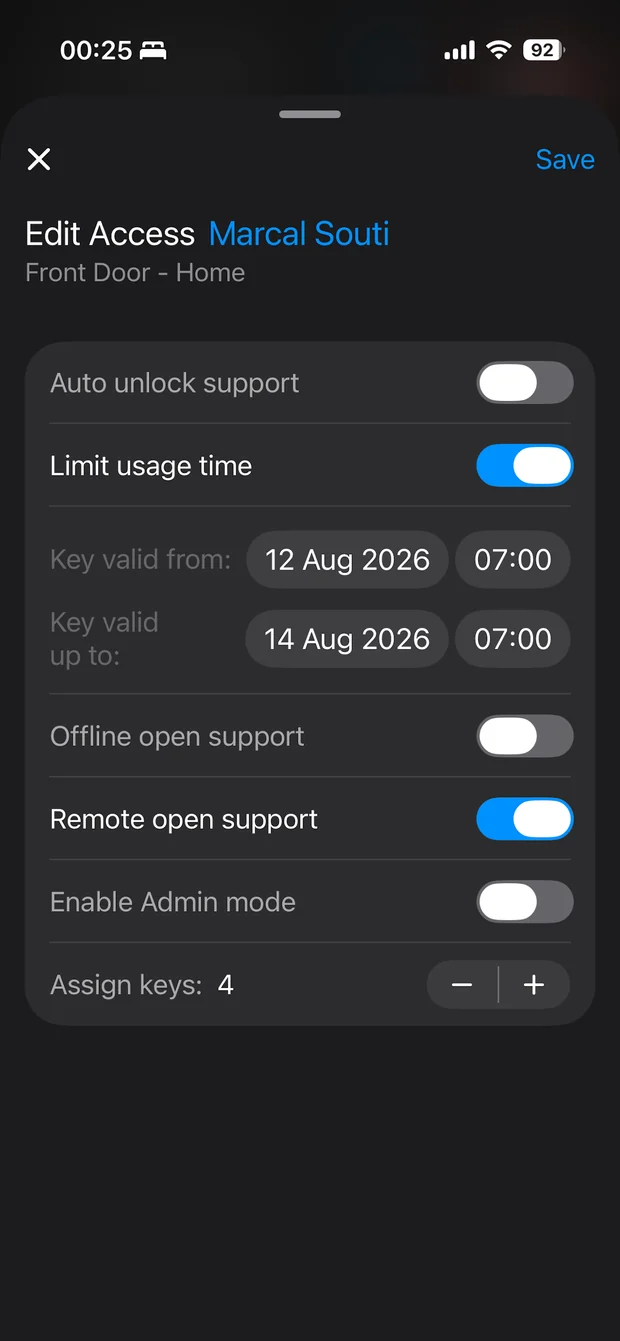
Every digital key has a start and an end. Offline keys only work within their own validity period, so a forgotten key closes itself.
Two-step login, one phone
Logging in needs your password and a code by e-mail. Your session is then tied to your own phone and stored in its secure keychain.
Revocation in real time
Change someone’s rights or block an account, and every phone receives the change immediately. No cylinder to replace, no key to collect.
Separation by design
Every customer has an isolated SafeXS system with its own database. One customer’s data never mixes with another’s.
Your data stays yours
SafeXS only collects what is needed to open doors safely, and you, as the owner of the lock system, decide what is kept and for how long.
- Your own system. Your lock system runs on your own server, on a cloud server in your name, or on European servers hosted by us.
- Encrypted where it matters. E-mail addresses and the learned positions of locks are stored encrypted on the server.
- Logging you configure. Choose whether the history shows names or stays anonymous, and how long log entries remain available.
- Visitor snapshots are temporary. BellXS deletes the snapshot of a visitor automatically after 14 days.
- No tracking, no advertising. The apps contain no advertising and we never sell your data. This website uses no tracking cookies and no analytics at all.
 Built for the GDPRDesigned according to the GDPR principles: data minimisation, purpose limitation and storage limitation.
SKG*** certified cylinders
Our smart cylinders carry three SKG stars, the highest burglary-resistance class for cylinders in the Netherlands, tested by SKG-IKOB according to NEN 5089.
- Five minutes of resistance against an experienced burglar with professional tools: the level of resistance class 3.
- Core-pulling protection, a requirement that two-star cylinders do not have to meet.
- Helps you meet the requirements of the Dutch Police Quality Mark for Secure Housing (Politiekeurmerk Veilig Wonen) and of insurers.
No foreign cloud between you and your front door
SafeXS is developed in the Netherlands and runs where you decide. Opening a door never depends on a cloud service outside your control.
On your own server
Run SafeXS in your own server room or data centre. Ideal for municipalities and organisations with their own IT department and security policies.
In your own cloud
A cloud server in your organisation’s name, set up, secured and managed by us. You stay the owner of the server and of the data.
Hosted by SafeXS
We host your SafeXS system for you on European servers and take care of updates and maintenance. You only use the app.
Questions about security
Can someone copy my digital key?
No. Every opening uses a new, signed command with a one-time code, and your account only works on your own phone. Copying a command or a password is not enough to open a door.
What if the server is hacked or offline?
The locks are not on the Internet and check every command themselves. People with an offline key keep opening their doors while the server is unavailable.
Is Bluetooth secure enough?
Bluetooth is only the transport. The security comes from the encryption, signatures and one-time codes on top of it, which the lock verifies itself.
Who can see when I opened a door?
Only the administrators of your own lock system, and only if logging is switched on. They can also choose to log anonymously.
I found a security issue. Where can I report it?
Thank you! Please e-mail us at info@safexs.eu. We investigate every report and keep you informed.
Want to know more about our security?
We gladly walk your IT or security officer through the architecture of SafeXS.